
Architecting Agentic AI in Enterprise Logistics: System Patterns, Guardrails, Vendor Ecosystem, and Production Realities
The deployment of generative AI in enterprise supply chains has evolved beyond basic document parsing and chatbot interfaces. Modern logistics platforms require Agentic AI—autonomous systems capable of perceiving environmental inputs, reasoning across multi-constraint domains, executing API tool calls, and resolving operational disruptions proactively.
This article synthesizes key operational blueprints, system prompt guardrails, failure modes, real-world vendor implementations, and a step-by-step roadmap for building enterprise-grade logistics agents.
1. Industry Scale & Market Friction
Enterprise supply chains operate under heavy communication volume and structural fragmentation:
High Unstructured Volume: Global carriers handle hundreds of thousands of operational emails and millions of voice-dispatch minutes annually.
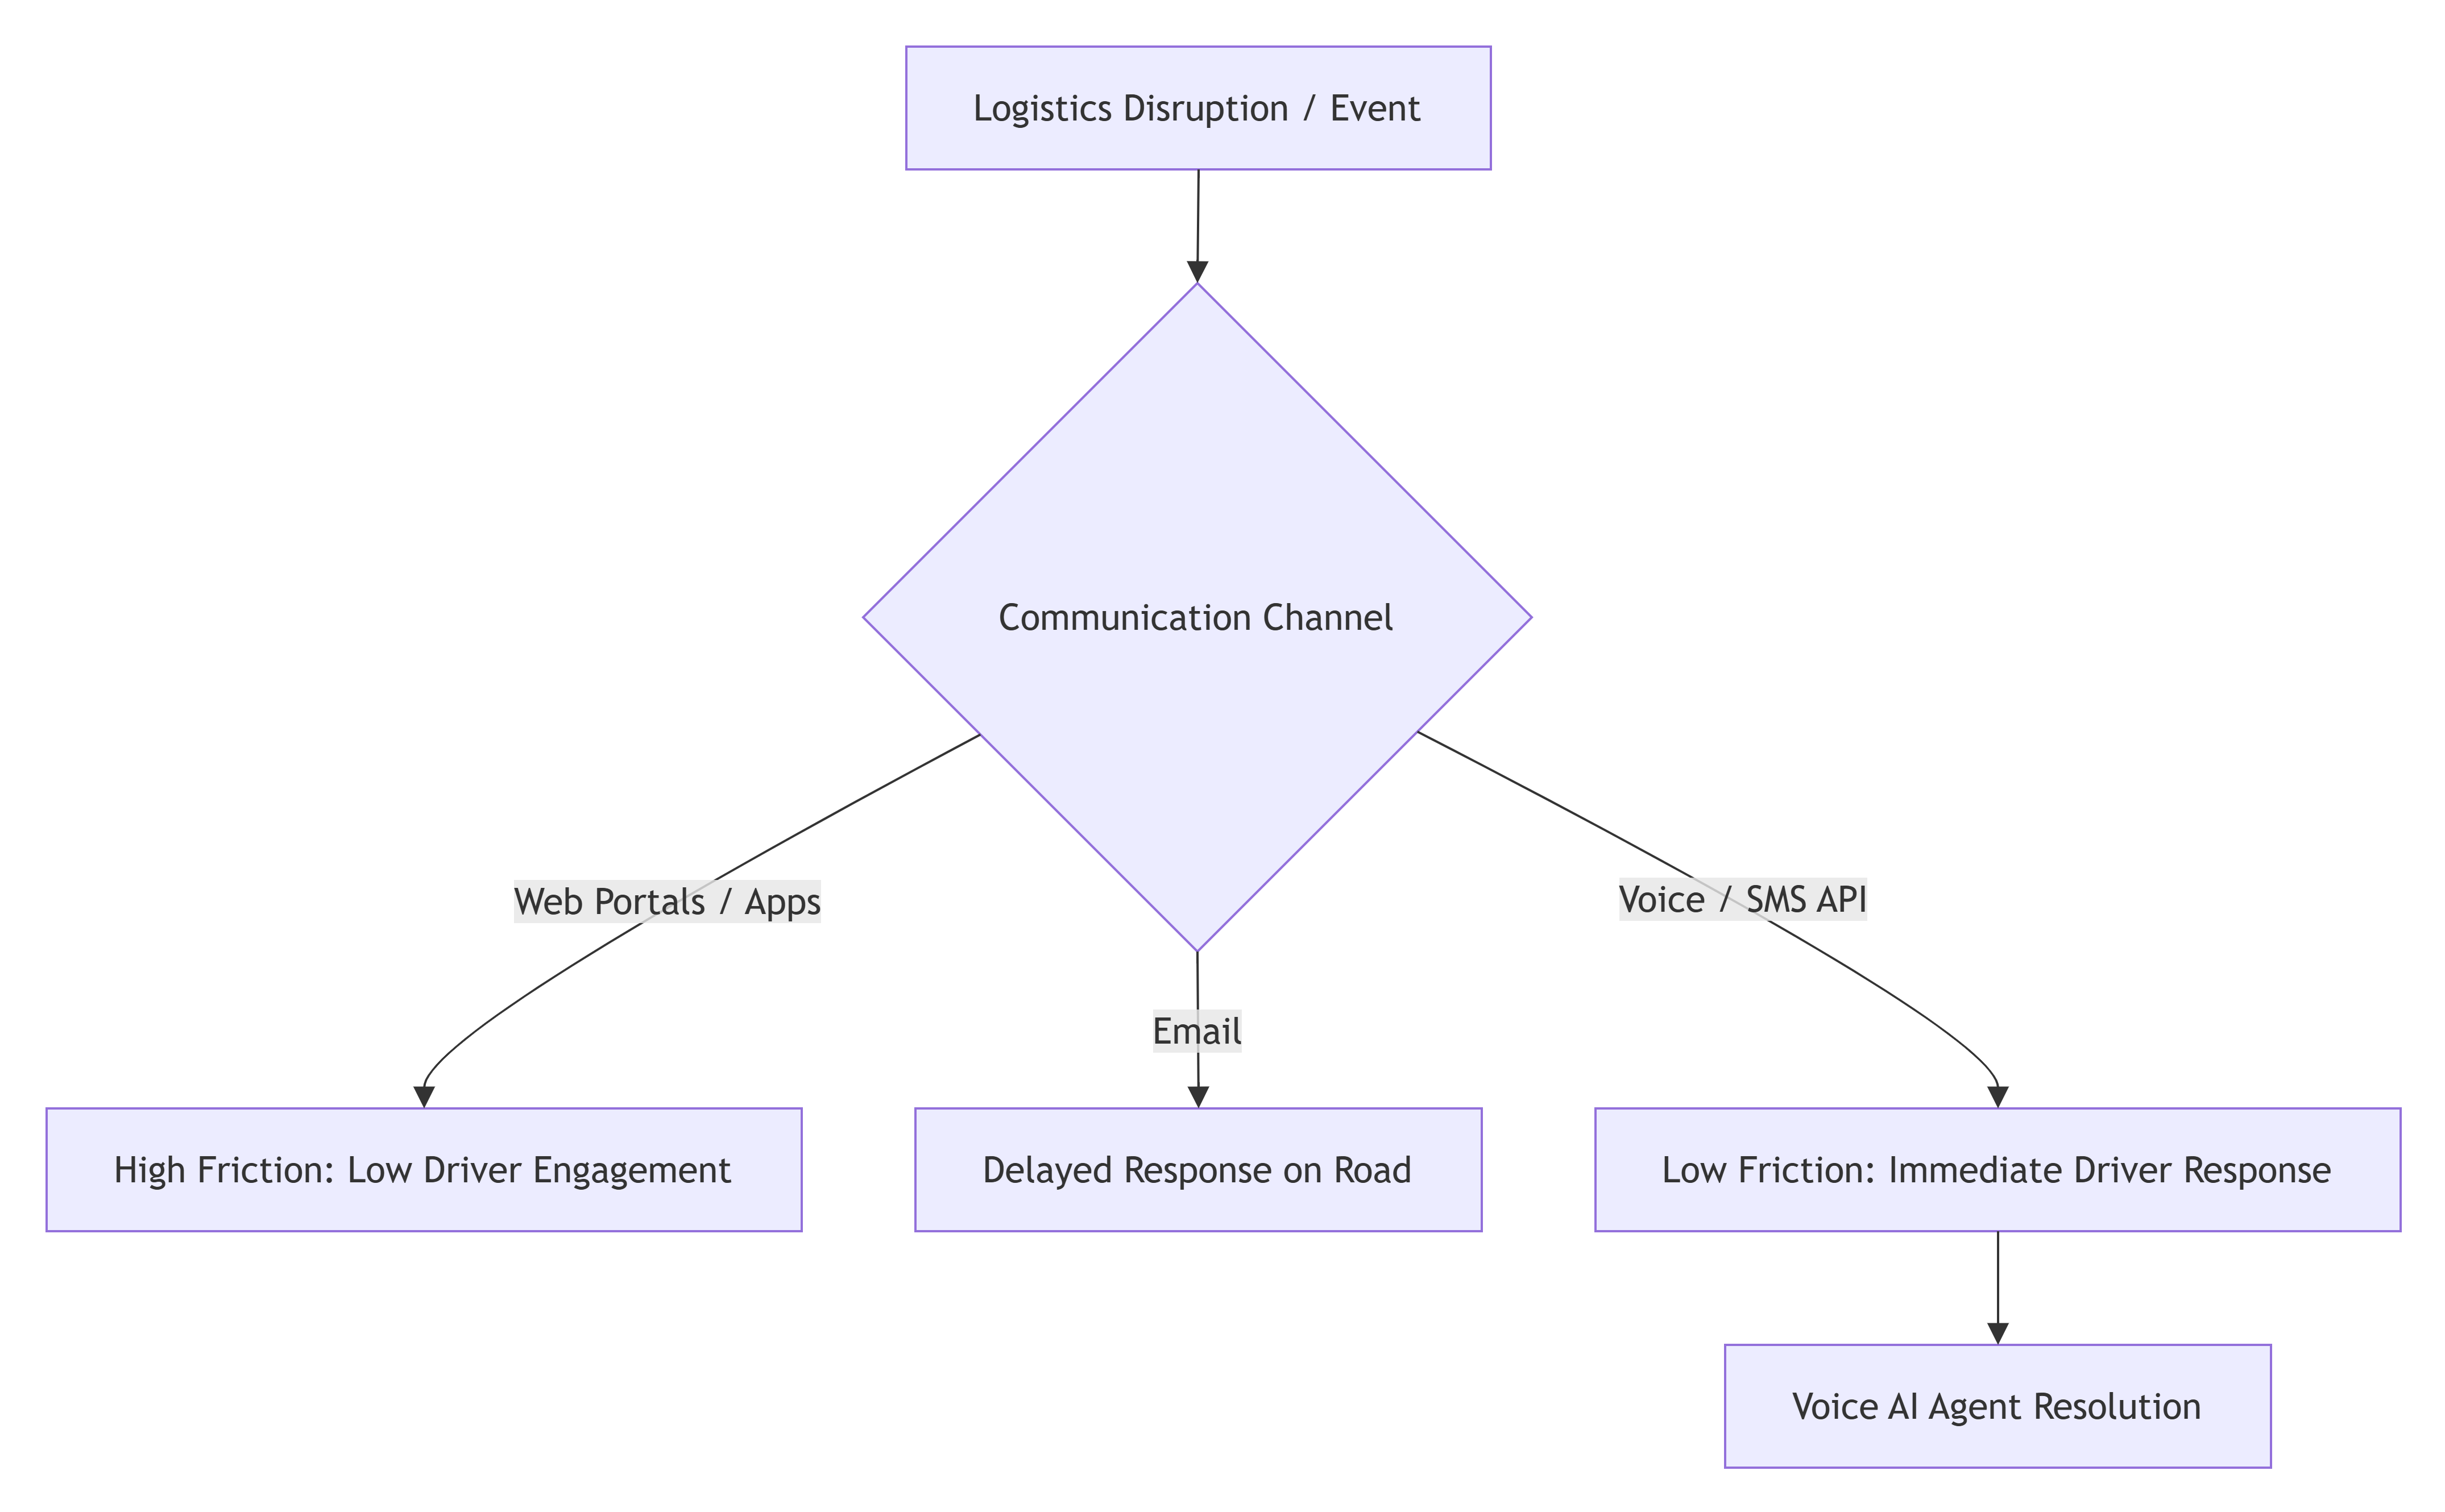
Channel Friction in Fragmented Markets: Over 80% of the freight market consists of independent operators running fleets of 1 to 5 trucks. These operators rarely log into proprietary web portals or check emails while en route. However, drivers consistently answer phone calls.
The Voice AI Advantage: Autonomous voice and conversational agents succeed by meeting carriers on their existing channels (Voice/SMS APIs) to handle routine appointment scheduling, driver follow-ups, and dock coordination.
2. High-ROI Use Cases & Strategy
Rather than attempting broad domain automation, agentic workflows pay off fastest when focused on targeted operational bottlenecks:
Initial Selection Framework
When selecting the first agentic process to automate, use a two-variable selection matrix:
High Frequency: Select workflows occurring hundreds of times per week to amortize initial setup and orchestration costs over high transaction volume.
Low Blast Radius: Choose processes where an agent error results in an embarrassing oversight (e.g., an unnecessary follow-up email) rather than an expensive operational failure (e.g., misquoted freight rates or lost customs status).

3. Production Architecture: "The Pattern to Copy"
To ensure predictable behavior across real-time freight networks, agentic systems should adhere to a simple, event-driven pattern:
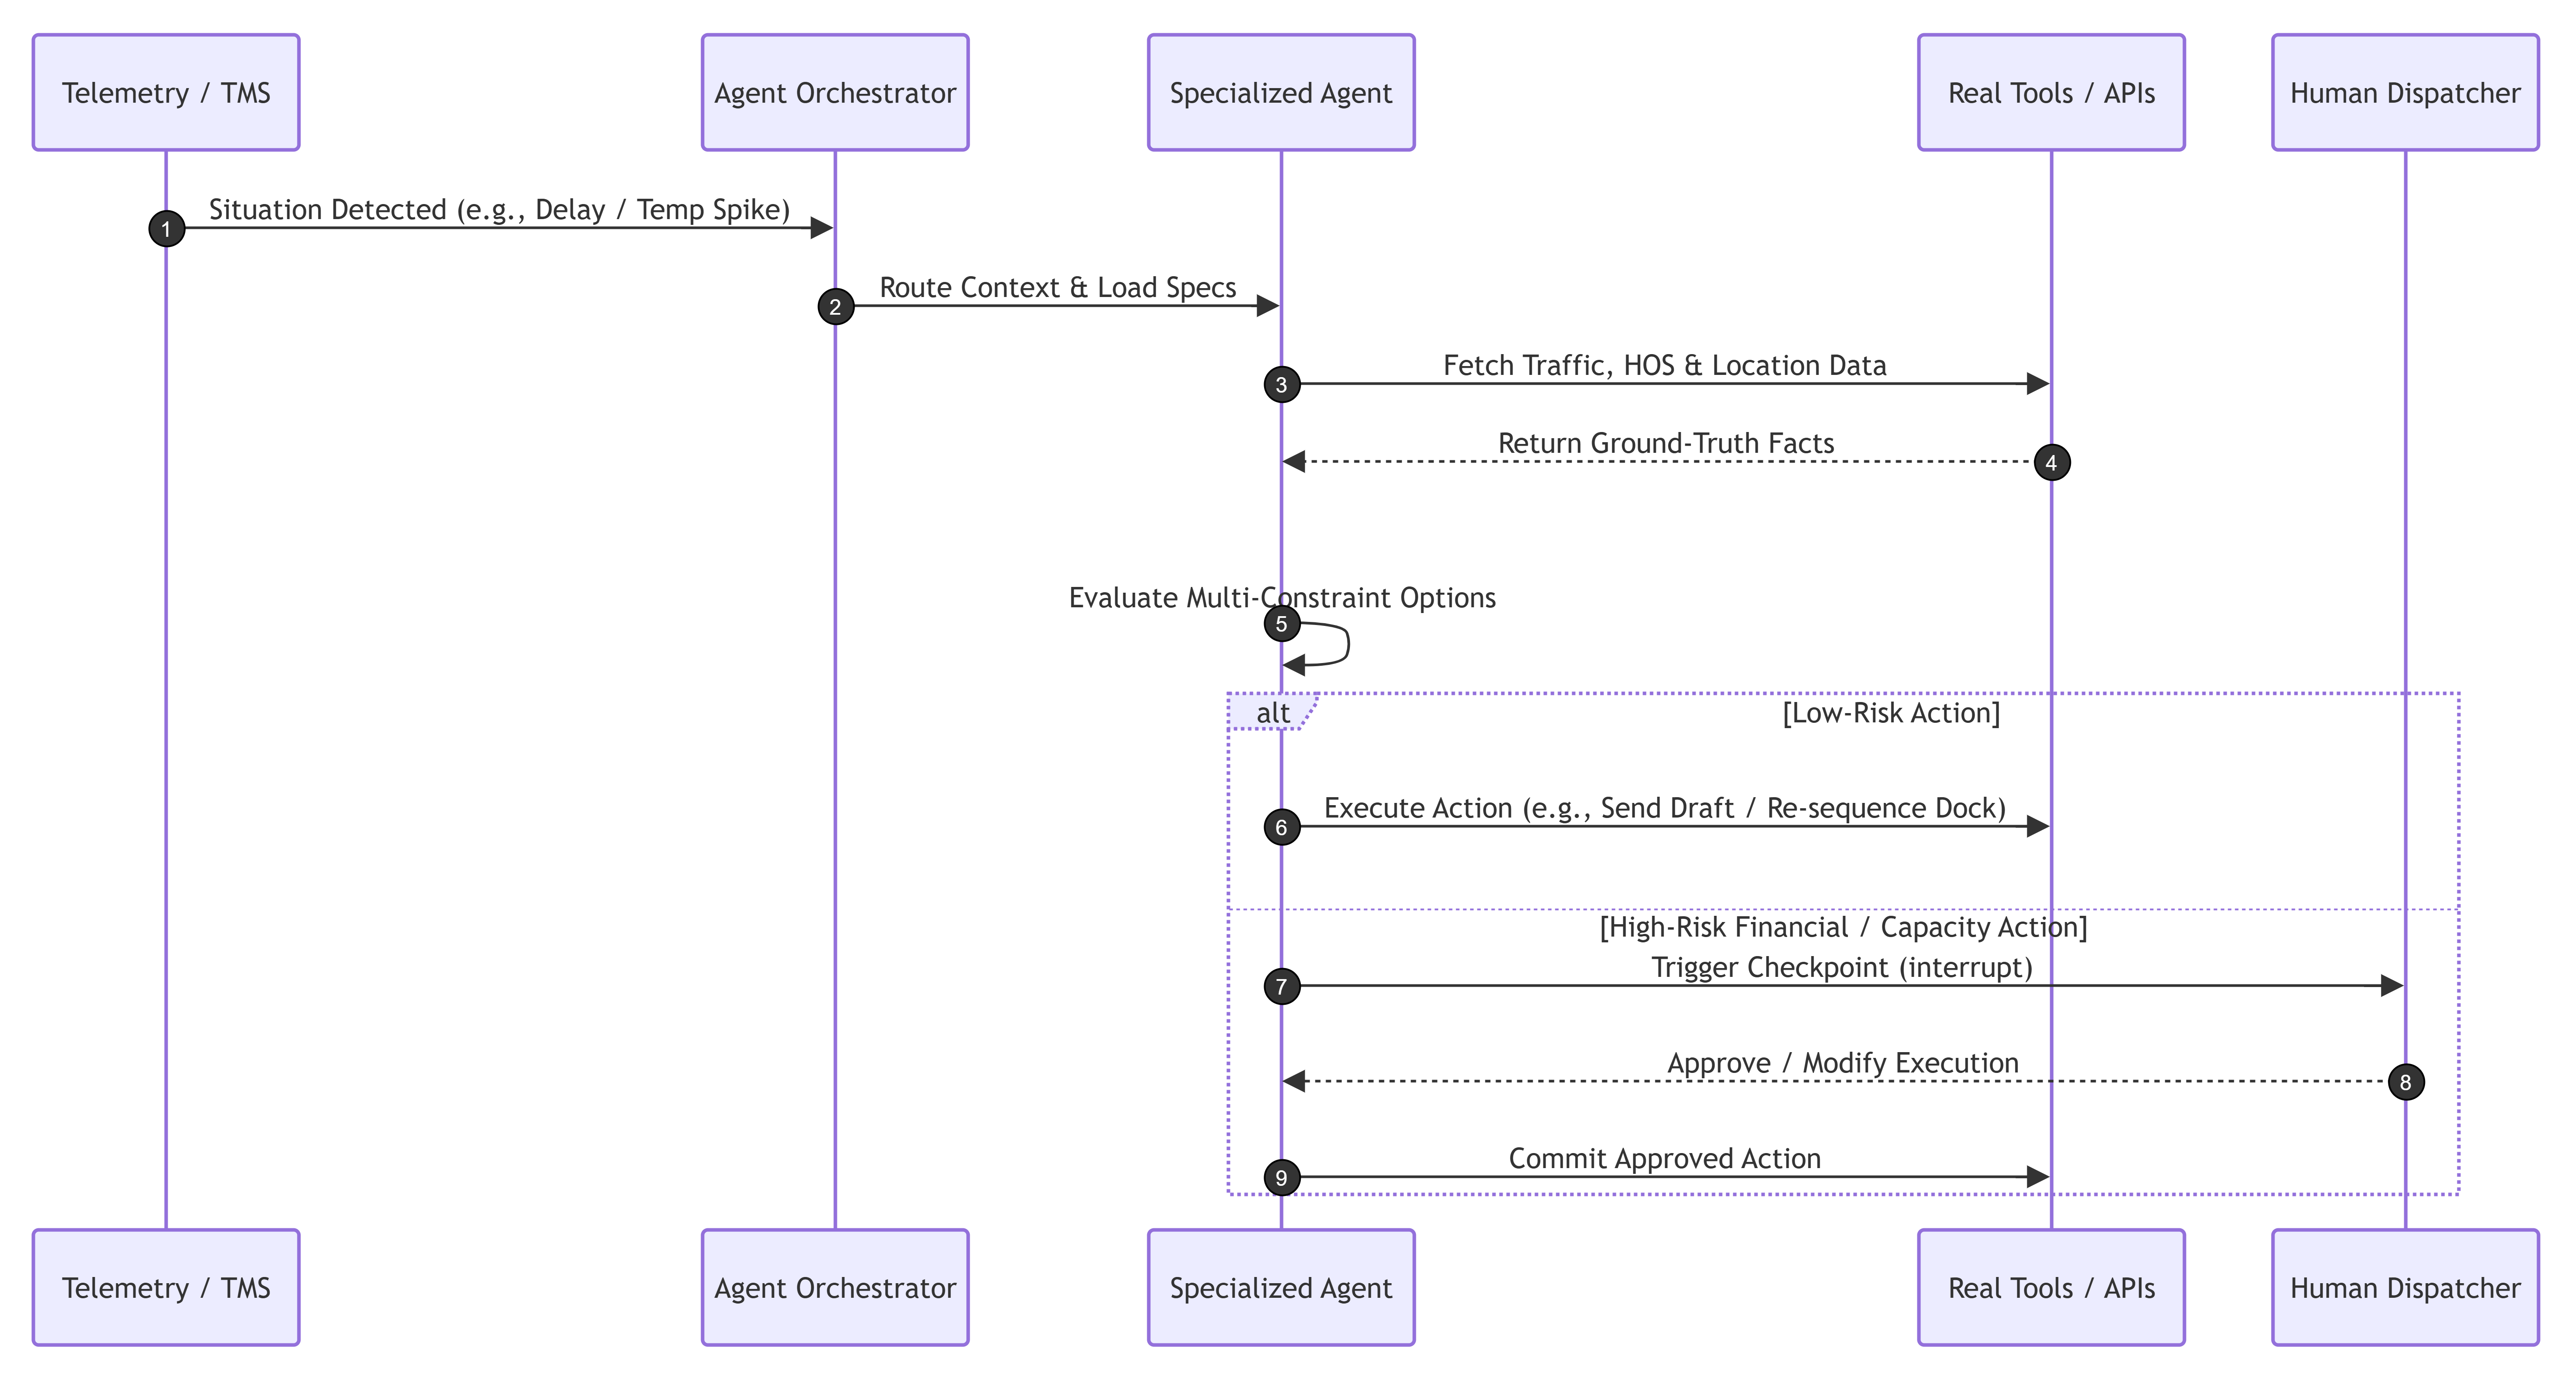
Action over Alerts: Agents must execute resolution paths (e.g., re-booking capacity, dispatching notifications) rather than generating passive dashboard alerts.
Context-Driven Autonomy: Action selection dynamically responds to real-time ground truths (traffic delays, cold-chain temperature limits, driver hours-of-service).
Single-Responsibility Micro-Agents: Maintain narrow agent scopes—such as separate micro-agents for Route Analysis and Carrier Communication—rather than a single monolithic model.
4. Hard Guardrails & Code Implementation
To prevent financial and legal liability, LLM agents require deterministic boundaries enforced directly at the prompt and framework level.
System Prompt & Execution State Flow
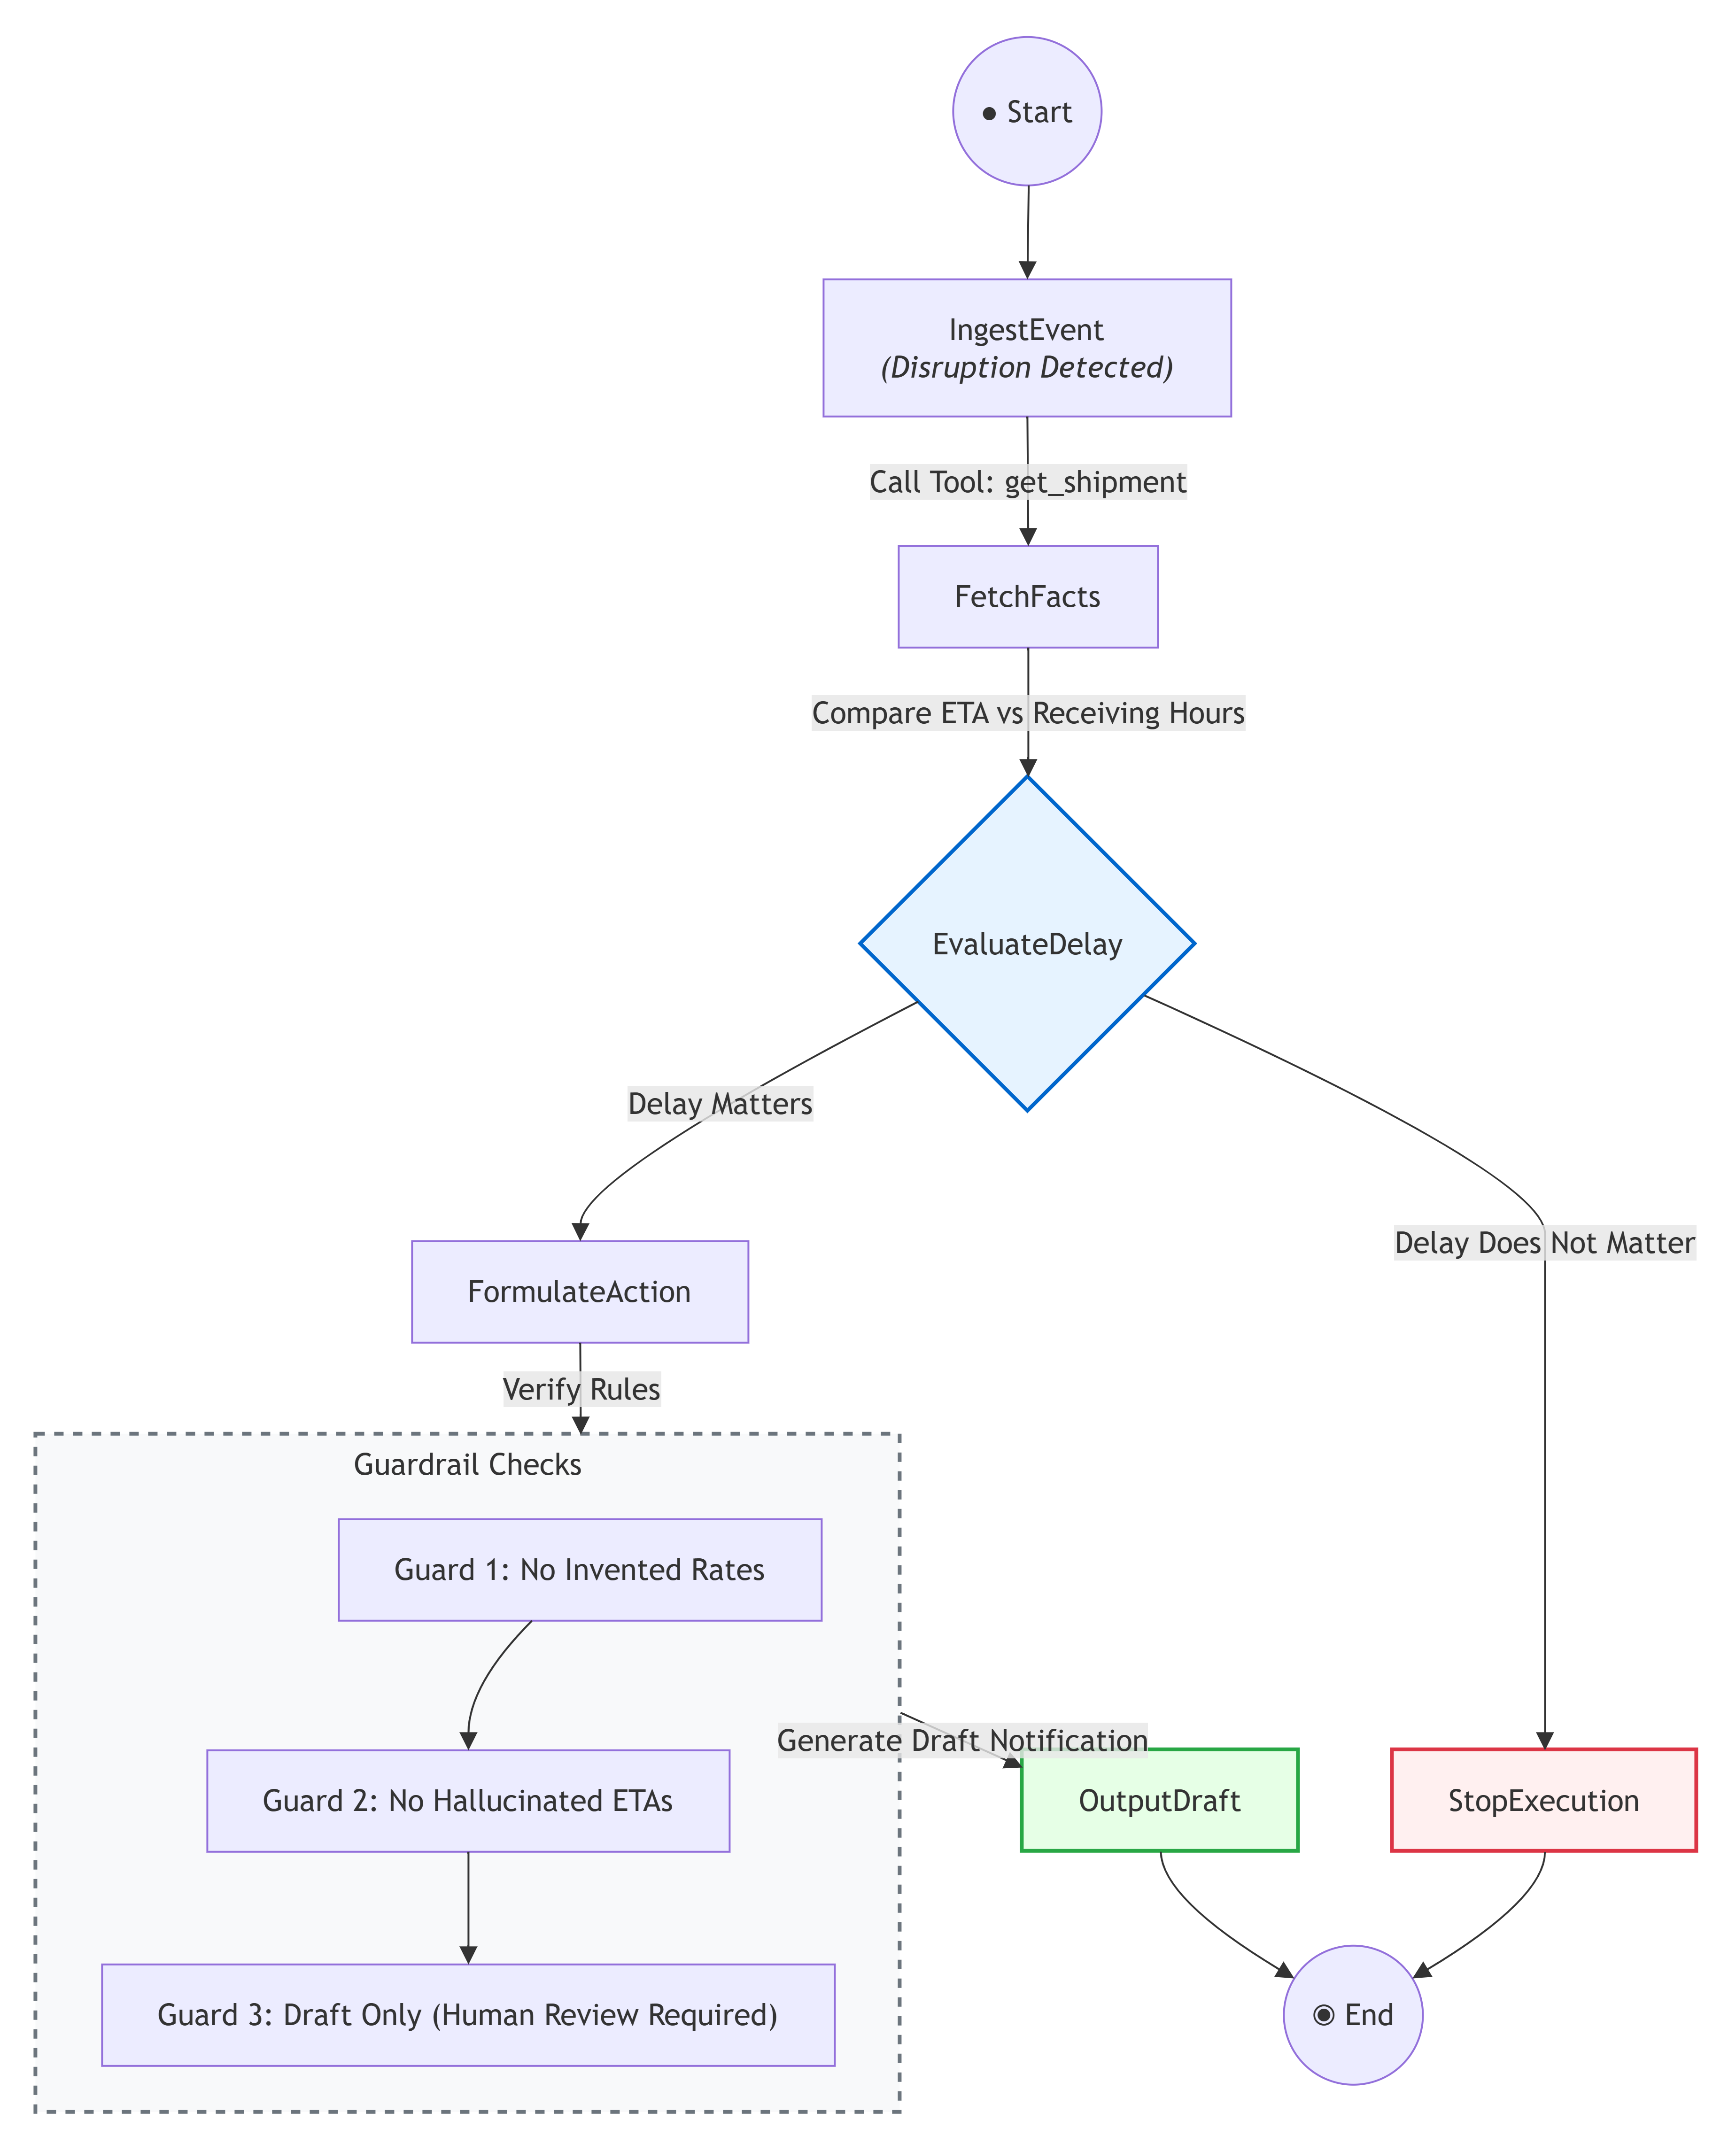
Prompt Enforcement
System prompts must explicitly restrict parametric hallucination:
from langgraph.prebuilt import ToolNode, tools_condition
from tools import get_shipment, check_traffic, send_customer_email

TOOLS = [get_shipment, check_traffic, send_customer_email]

SYSTEM = """You are a freight operations agent for a US truckload carrier.

When a shipment is at risk, find out what is actually going on before you do
anything. Judge whether the delay matters against the promised arrival and the
customer's receiving hours. If it matters, notify the customer with a short,
specific message. If it does not matter, say so and stop.

Never invent a rate, an arrival time, or a reason for a delay. If you need a fact,
use a tool to get it."""

llm = ChatAnthropic(model="claude-sonnet-5", max_tokens=2048).bind_tools(TOOLS)
Specialized Sub-Agent Workflows
In orchestrated multi-agent environments, distinct markdown prompts govern sub-agent behaviors:
Route Analysis Sub-Agent: Analyzes route options (wait, reroute, split load, re-cover) against transit time costs. Enforces strict factual constraints: Read shipment details from project files. Never invent distances, transit times, or road conditions.
Carrier Communication Sub-Agent: Formulates direct outreach messages. Enforces strict policies: Never quote a rate, never promise delivery times unsupported by routing analysis, and keep customer messages under 90 words. All outputs default to Draft Only status for human approval.
5. Production Limits & Mitigation Strategies
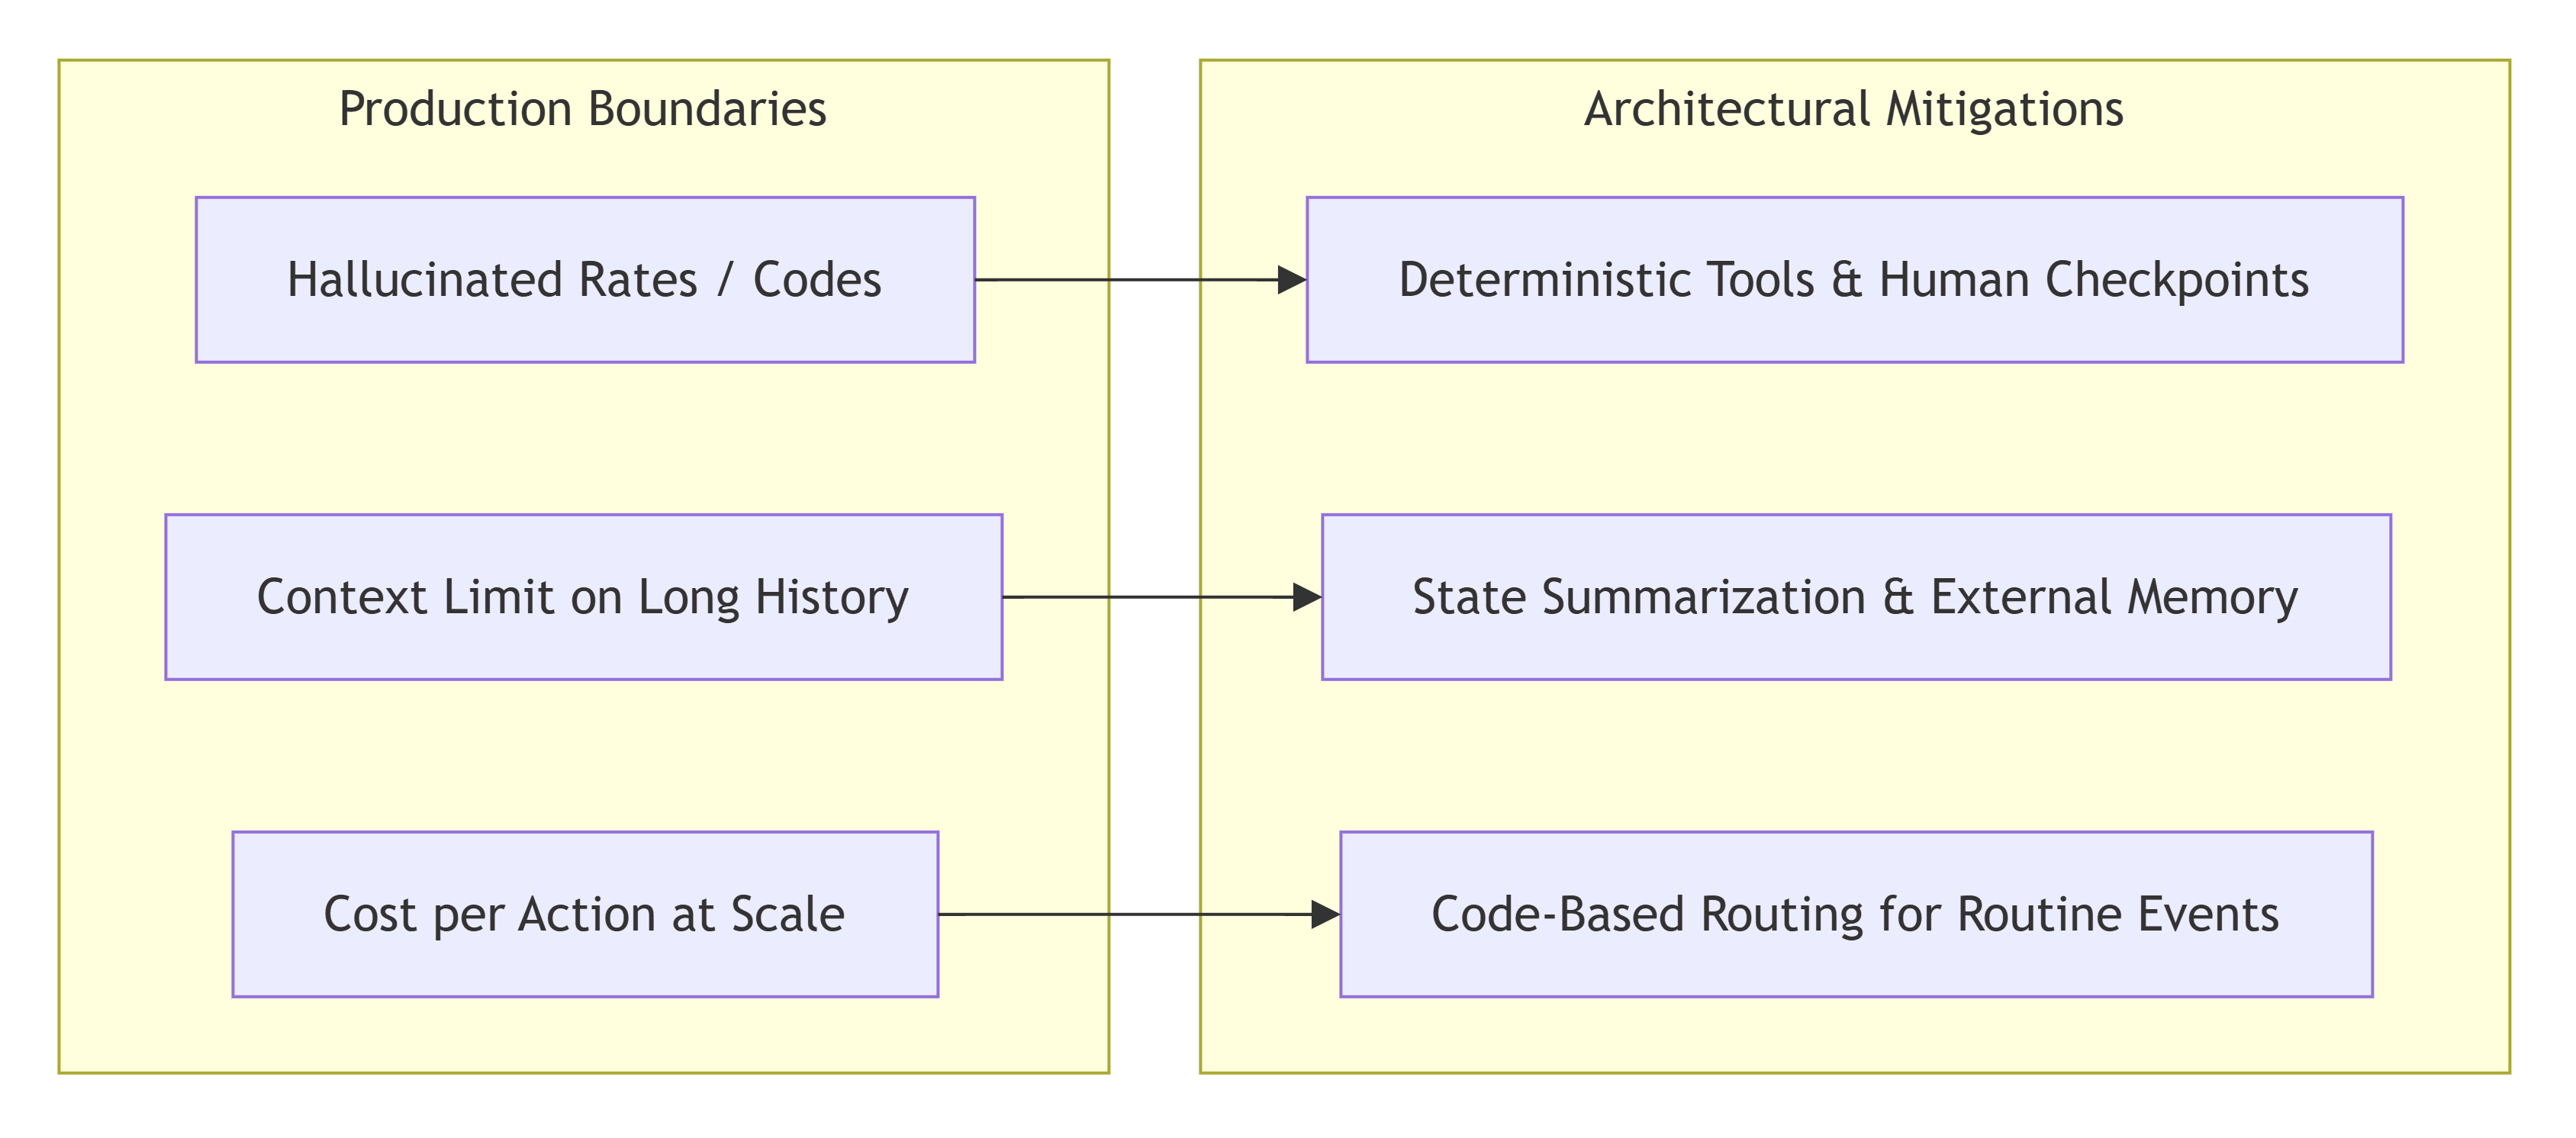
Architecting logistics agents for enterprise scale requires planning around three core technical limits:
| Production Boundary | Operational Impact | Mitigation Architecture |
|---|---|---|
| Hallucinated Rates & Customs Codes | Invalid HS codes or false rate quotes cause regulatory fines and direct financial losses. | Require API tool verification for all factual queries; gate financial commitments behind Human-in-the-Loop (interrupt()) steps. |
| Context Limits on Long Histories | Multi-stop loads generate extensive telemetry, tracking logs, and check calls that overwhelm LLM context windows. | Summarize graph state, prune chat histories in memory states, and persist raw telemetry in external relational/vector storage. |
| Cost per Action at Scale | Unchecked LLM reasoning loops over routine telemetry updates inflate API execution costs. | Restrict LLM invocations to exception-handling triggers; process standard status updates through deterministic code paths. |
6. Vendor Ecosystem Alignment
Leading logistics technology providers specialize across different operational layers of the agentic stack:
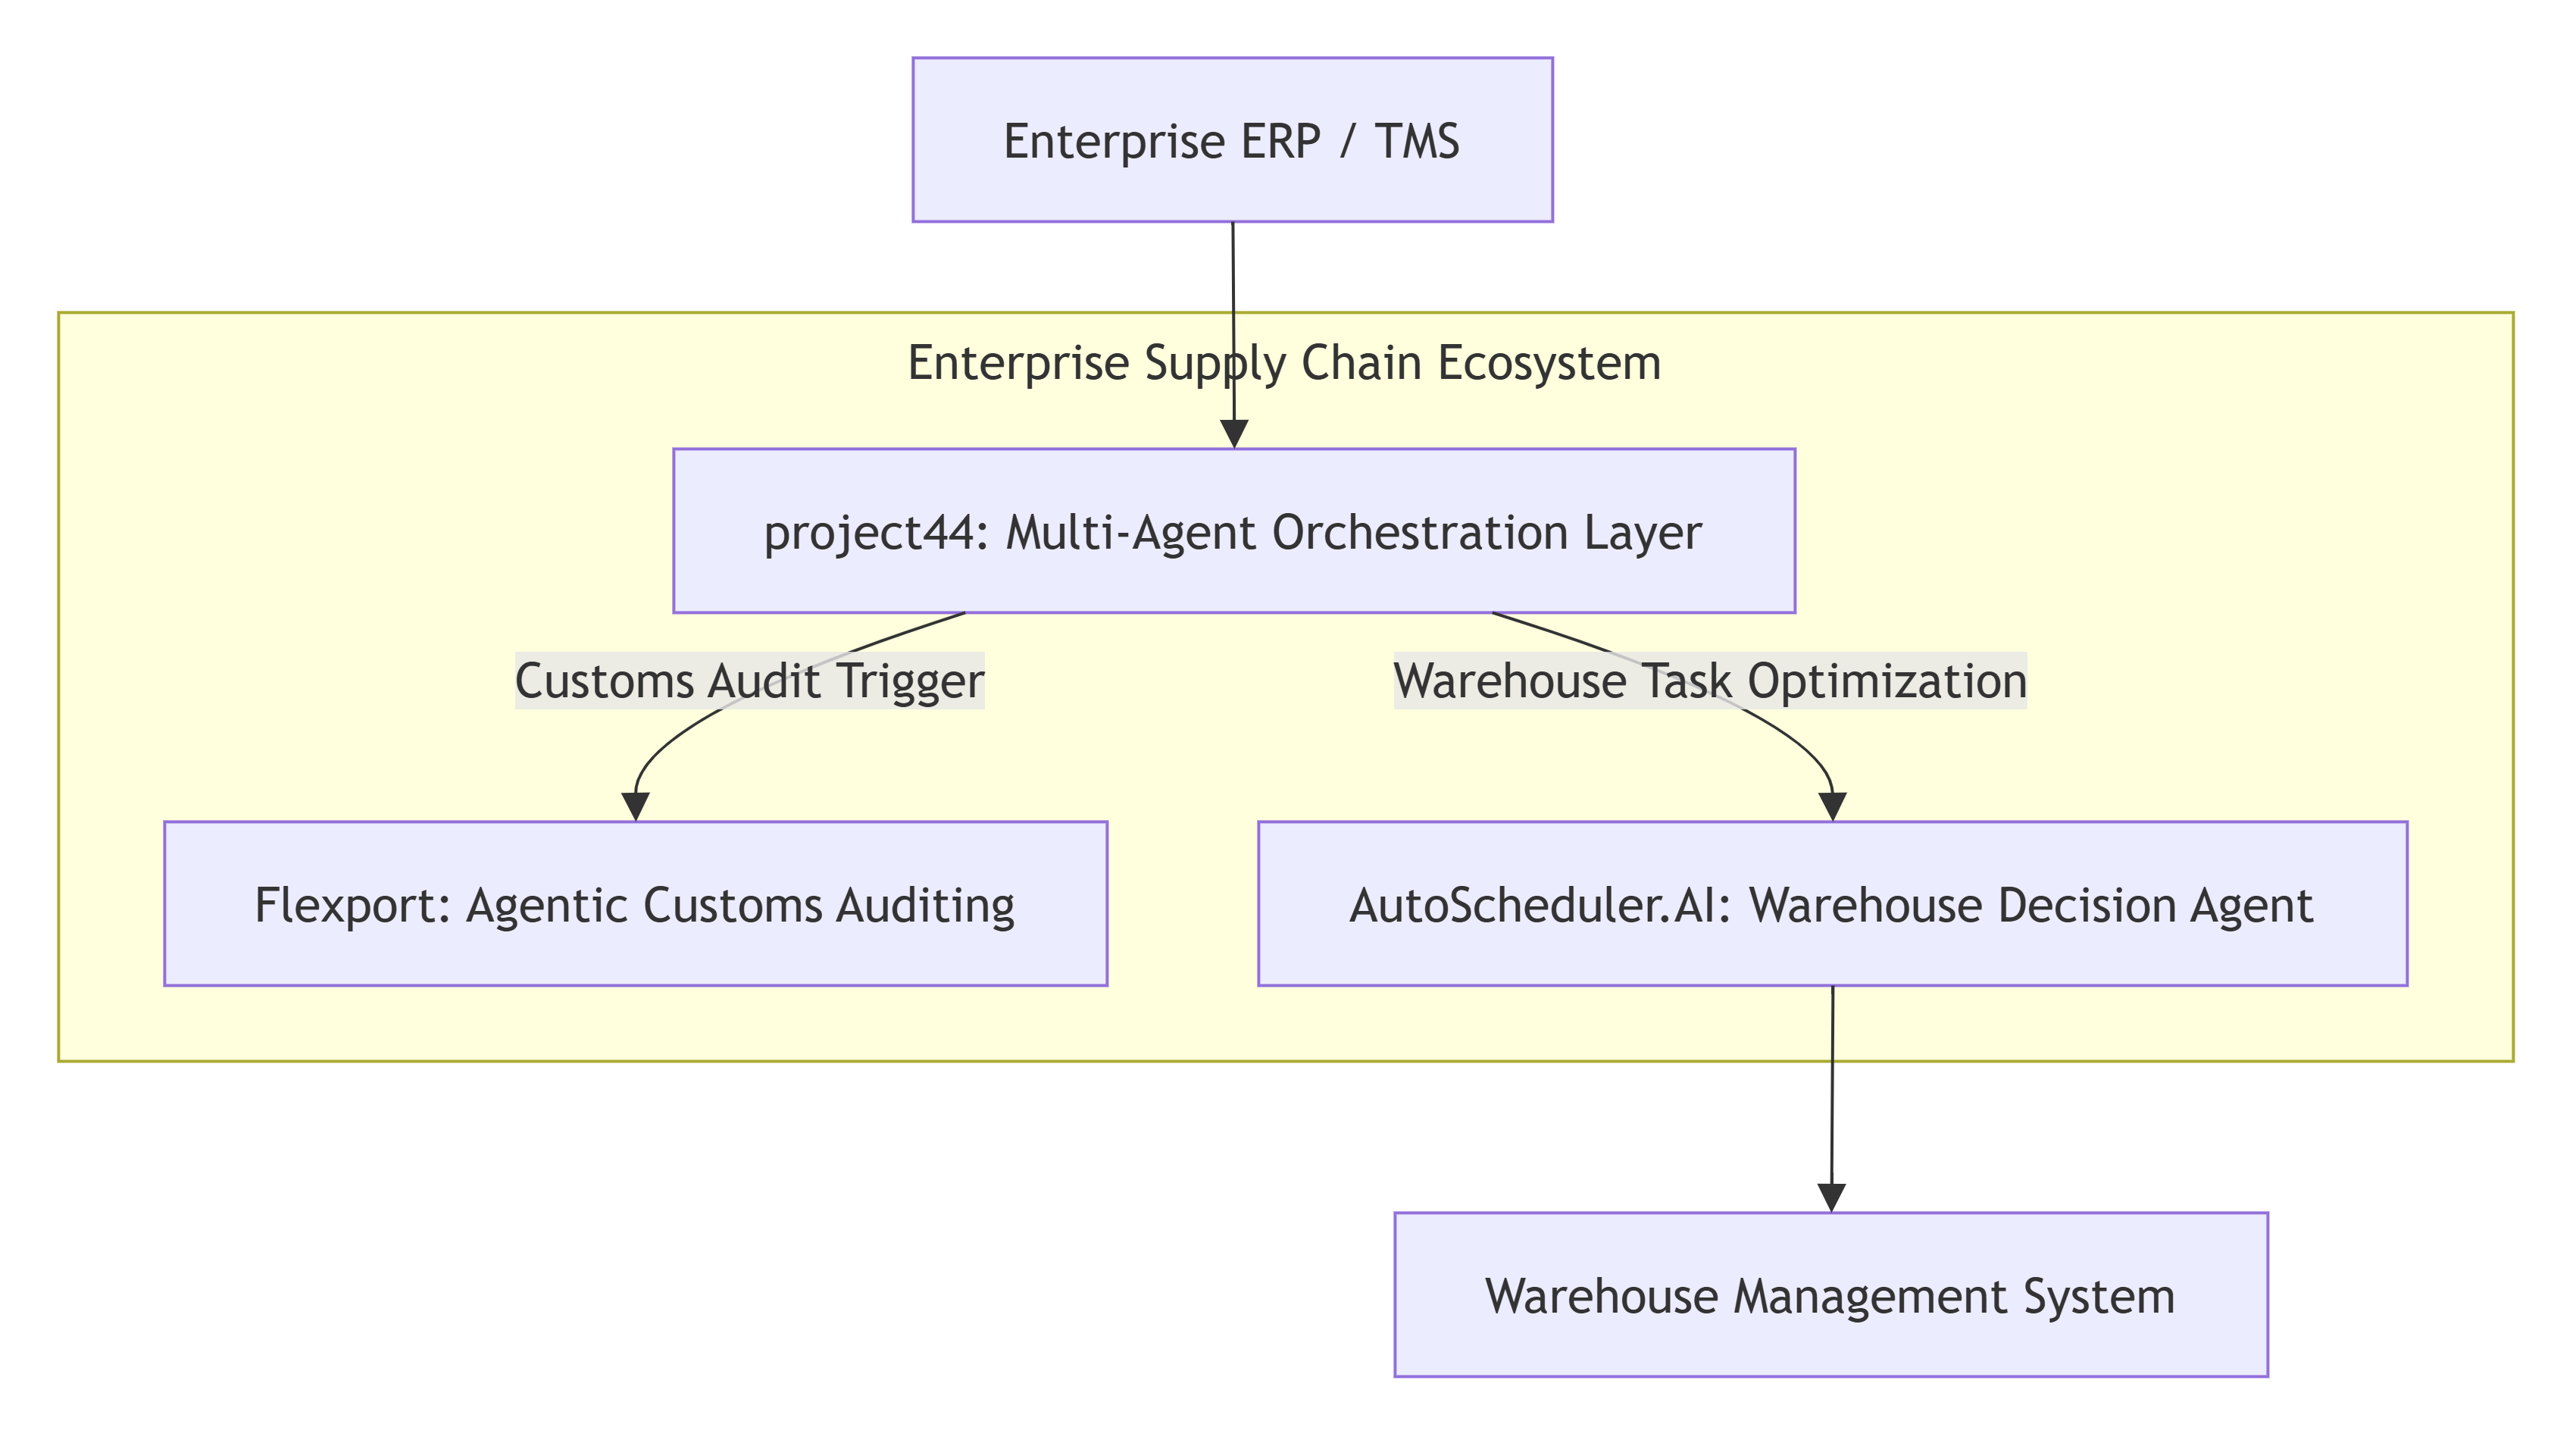
Flexport (Agentic Customs Auditing): Deploys compliance agents that scan historical customs entries to identify tariff errors, incorrect Harmonized System (HS) classifications, and duty overpayment refund opportunities.
project44 (Multi-Agent Orchestration): Coordinates multi-agent workflows across ocean, rail, and over-the-road networks—linking disruption detection agents with routing and carrier engagement agents.
AutoScheduler.AI (The Warehouse Decision Agent): Sits as an intelligent decision layer above existing Warehouse Management Systems (WMS) to resequence labor, dock allocation, and task prioritization in real time as operational exceptions occur.
7. Implementation Roadmap: Next Four Steps
To transition agentic logistics from concept to production, execute this four-phase adoption framework:
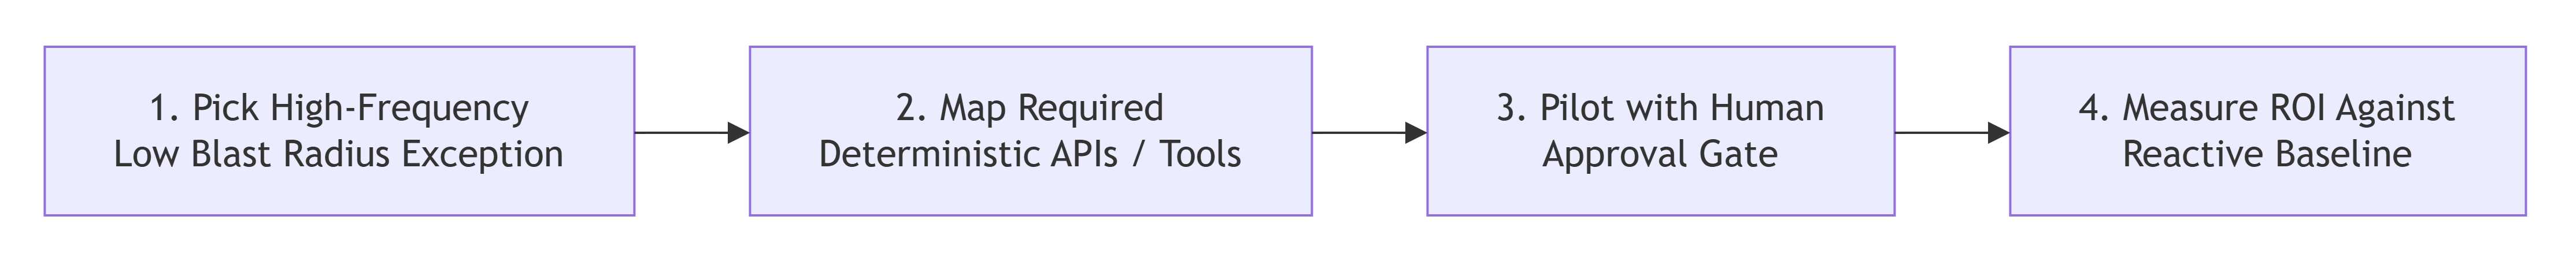
Pick One High-Frequency Exception: Identify a single operational scenario occurring many times per week where errors carry low financial blast radius (e.g., chasing carrier status updates or auditing linehaul documentation).
List the Tools the Agent Needs: Map out the exact deterministic APIs, database connectors, and external lookup services required for the agent to retrieve ground-truth facts without hallucination.
Pilot with an Approval Checkpoint: Deploy the agent with mandatory Human-in-the-Loop gates (
interrupt()) for high-stakes decisions (e.g., committing budget, rebooking capacity, or issuing customer notifications).Measure Against Your Reactive Baseline: Evaluate performance metrics—such as time to exception resolution, manual effort reduction, and exception recovery speed—against traditional manual processes.
Executive Summary
Logistics runs on exceptions, and agentic AI represents the first wave of systems capable of perceiving, reasoning, and acting on operational disruptions rather than merely reporting them on dashboard alerts.
Enterprise platforms like Uber Freight, DHL, and Flexport actively run autonomous workflows in production. To ensure safety and ROI:
$$\text{Production Agent} = \text{Narrow Job} + \text{Real Tools} + \text{Human Accountability for Big Calls}$$
Let agents act autonomously on reversible work, enforce approval checkpoints for financial commitments or capacity changes, and start implementation with a single high-frequency exception scenario.