
Intent Intelligence: Adapting Amex's Agentic Commerce Framework for Enterprise FinOps and Multi-Cloud Governance
As AI agents transition from passive conversational advisors to autonomous enterprise actors, the software ecosystem faces a critical paradigm shift: how do we grant AI systems execution authority without exposing core infrastructure to runaway agentic loops, hallucinated state changes, or prompt injection attacks?
The industry's initial response—relying on post-execution logging or hoping probabilistic LLMs "behave themselves"—is fundamentally insufficient for regulated enterprise environments.
American Express highlighted this exact challenge in its Intent Intelligence Framework for Trusted Agentic Commerce, one of five core services in the Amex Agentic Commerce Experiences (ACE) Developer Kit. Amex's core architectural insight is simple yet profound: shift user intent verification upstream, capturing and cryptographically scoping authorized constraints before an agent executes a transaction.
By combining Amex's Intent Intelligence model with Cryptographic Action-Binding (H_A == H_B) and deterministic policy execution gates, this project adapts the framework to secure enterprise cloud infrastructure, FinOps, and automated provisioning pipelines.
1. The Core Problem: The Autonomous Execution Gap
Standard agentic workflows suffer from an architectural flaw: the probabilistic reasoning layer is directly coupled to the execution runtime.
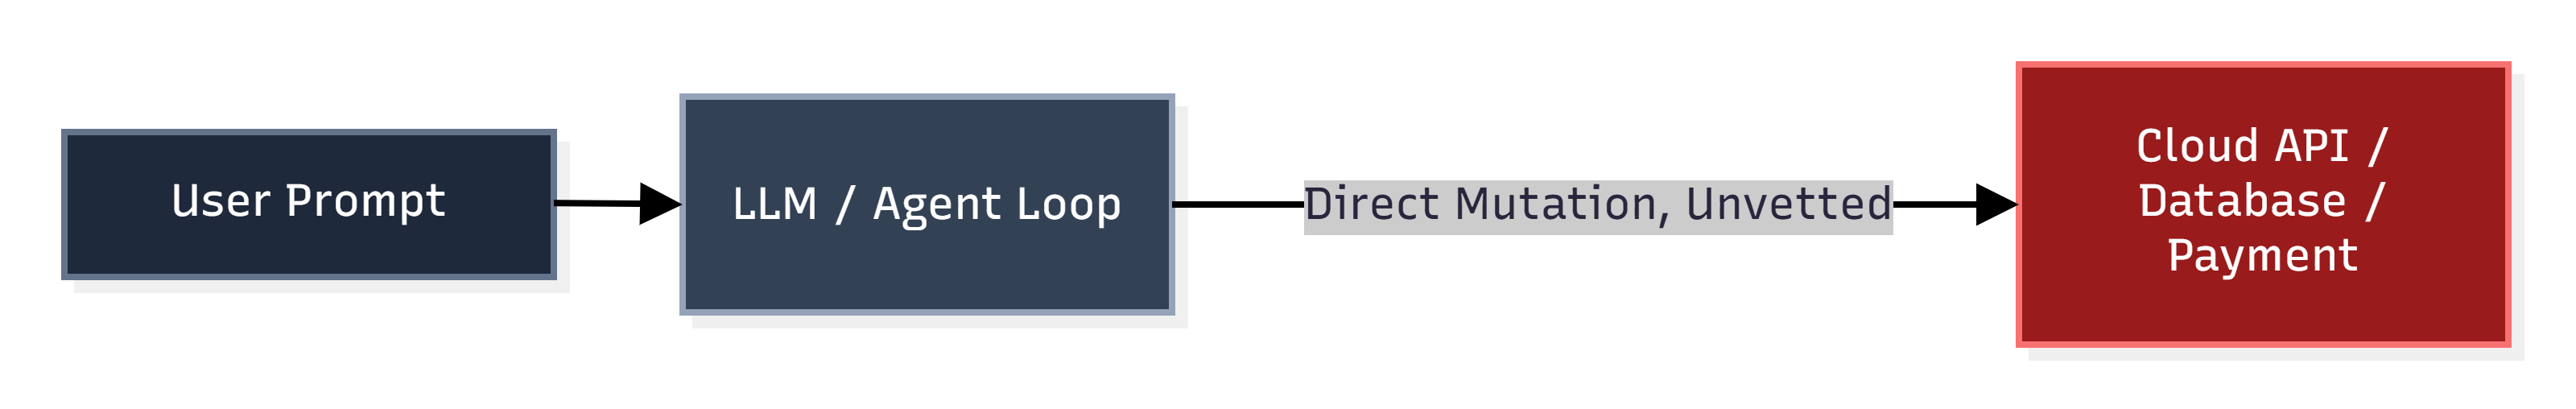
When an agent is allowed to reason, construct payloads, and directly invoke tools or cloud endpoints (e.g., Terraform, GCP APIs, Azure Resource Manager), any prompt drift, model failure, or injection attack leads to immediate, unvetted state mutations.
In consumer commerce, this manifests as unauthorized purchases. In enterprise FinOps, it manifests as unauthorized infrastructure scaling, deleted production databases, or regional compliance breaches.
2. Amex Intent Intelligence: The 4-Stage Control Pattern
American Express addresses this by introducing a mandatory Intent Phase that precedes the Execution Phase:
Create & Confirm Intent (Create Intent API): Captures explicit user instructions and boundary constraints—such as maximum budget ceiling, allowed merchant/provider, and target action—before any transaction starts.
Establish Proof of Intent: Generates a unique Intent ID and a cryptographically signed Proof of Intent Token representing the user's explicit authorization payload (H_A).
Scope Execution Credentials: The token scopes the operational credentials used during checkout or execution, ensuring downstream systems refuse actions that breach authorized parameters.
Apply Intent Throughout Lifecycle: The Intent ID and Proof Token act as inline controls across every subsequent hop, verifying that requested actions (H_B) match authorized intent (H_A) prior to state mutation.
3. Translating Amex Intent Intelligence to Multi-Cloud FinOps Governance
When applied to enterprise cloud orchestration—such as provisioning Azure Verified Modules (AVM) or GCP Cloud Foundation Toolkit modules—the Amex Intent Intelligence architecture transforms into an Inline GovOps Action Gate.
4. Complete End-to-End Execution Dataflow
This state diagram details how an incoming natural language intent transitions through JWT issuance, cryptographic hash verification, deterministic rule validation, and Terraform CLI execution.
5. Comparative Matrix: Traditional Agents vs. Intent-Gated Architecture
| Architectural Feature | Traditional Agentic Architecture | Amex Intent Intelligence / GovOps Action Gate |
|---|---|---|
| Execution Authority | Delegated directly to probabilistic LLM | Reserved for deterministic control plane |
| Constraint Timing | Evaluated post-execution or in-prompt | Evaluated upstream, prior to state mutation |
| Security Mechanism | System prompts & LLM guardrails | Cryptographic Action-Binding (H_A == H_B) & JWT tokens |
| Audit Trail | Unstructured conversational logs | Immutable Intent ID linked to hashed execution payloads |
| Malicious Injection Resilience | Low (vulnerable to prompt manipulation) | High (payload modifications fail hash check H_A == H_B) |
| Regulatory & FinOps Alignment | Probabilistic / non-deterministic | Zero-variance compliance & bounded budget ceilings |
6. Reference Implementation
This architecture is implemented as a working, open-source FastAPI service — not just a diagram:
🔗 sehgalnamit/govops-finops-action-gate
Cryptographic Action-Binding (
H_A == H_B), a deterministic FinOps/GovOps policy engine, and a Terraform execution layer, all independently unit-tested.A catalog of real, verified Terraform modules — not toy examples — spanning Azure Verified Modules (
resource_group,virtual_network,storage_account,key_vault) and GCP Cloud Foundation Toolkit modules (cloud_storage,vpc_network,cloud_sql_postgresql).A zero-cost demo path: when the Terraform CLI or cloud credentials aren't available, the gate transparently falls back to a simulated
terraform plan, so the full intent → crypto-binding → policy-gate → execution flow can be run end-to-end with no cloud account and no spend.Clone it, run
pytest tests/, and inspectGET /api/v1/catalogto see the full set of gated infrastructure modules.
Conclusion
The release of American Express's Intent Intelligence Framework marks an industry milestone: it formalizes the shift from unconstrained model autonomy to intent-bounded execution.
Whether applied to consumer payment rails or enterprise multi-cloud FinOps, the core engineering imperative remains identical: never grant a probabilistic model direct execution authority.
By leveraging LLMs for perception and orchestration (System 2) while enforcing state mutations through cryptographically bound, deterministic gates (System 1), enterprises can safely deploy agentic workflows at scale—maximizing speed while retaining absolute control over security, budget, and compliance.